Sunday, 18 September 2011

How to find the process that is using a TCP port

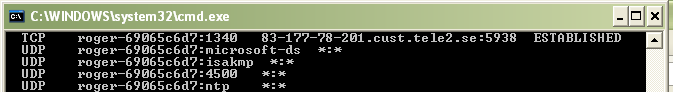
Earlier today I was inspecting all computers in my home for malware with the help of GMER and FreeFixer. I was also using the netstat command line tool to look for any suspicious network connections. Netstat shows established TCP connections and ports that are listening for incoming connections. There was one entry in the netstats output that looked a bit suspicious: A connection to a server at cust.tele2.se on port 5938 and cust.bredbandsbolaget.se, also on port 5938.


The problem with netstat is that I couldn't see the name of the executable file that had established this connection. As usual Sysinternals comes to the rescue. They offer a tool called TCPView which also shows the process name along with connection info. It turned out that TeamViewer that I recently installed had established the cust.tele2.se:5938 connection:


Another alternative to find the process name that owns a connection is to use netstat -o which will list the process identifier for each connection and compare it to the information listed in the Windows Task Manager.

Sunday, 12 September 2010

BUGCODE_USB_DRIVER

Seems like VMWare 5.5, iTunes and my new iPhone don't not mix. When I plugin in the iPhone I get the following blue screen:


The only work-around I could find to this problem was to install iTunes directly on the host machine :(

Friday, 30 April 2010

Desktop Security 2010 Scareware

Stumbled upon another rogue security application called Desktop Security 2010. It has been around for some time now. What's new about this one is that it adds a new column to the Windows Task Manager falsely claiming that some of my files are infect:

Wednesday, 7 April 2010

Your Protection Scareware

Stumbled upon a new scareware application called "Your Protection" today:


FreeFixer v0.55 log
http://www.freefixer.com/
Operating system: Windows XP Service Pack 2
Log dated 2010-04-07 14:20

Registry Startups (5 whitelisted)

HKCU\..\Run, Your Protection = "C:\Program Files\Your Protection\urpprot.exe" -noscan

Friday, 5 February 2010

SafePcAv Scareware

Ran into another scareware application today. It detects malware on a clean machine:


FreeFixer v0.53 log
http://www.freefixer.com/
Operating system: Windows XP Service Pack 2
Log dated 2010-02-05 16:13

Processes (21 whitelisted)
C:\Program Files\FreeFixer\freefixer.exe
C:\Program Files\SafePcAv Software\SafePcAv\SafePcAv.exe

End of FreeFixer log


Sunday, 31 January 2010

"Antimalware Defender" Scareware Disguised as a Windows Critical Security Update

Antimalware Defender is another scareware application. It pops up dialog boxes falsely claiming it is part of a Windows Critical Update:


Antimalware Defender reports lots of malware on a clean system:


You can use FreeFixer to remove AntiMalware Defender. I've pasted a FreeFixer log below which will help you identify the malware items:

FreeFixer v0.53 log
http://www.freefixer.com/
Operating system: Windows XP Service Pack 2
Log dated 2010-01-31 15:04


Browser Helper Objects

{fa217b17-bd53-4441-bc32-3de578a2826a}, {fa217b17-bd53-4441-bc32-3de578a2826a}, C:\WINDOWS\system32\fa217b17-bd53-4445-bc32-3de578a2826a_6.avi

Registry Startups (4 whitelisted)

HKLM\..\Run, fa217b17-bd53-4445-bc32-3de578a2826a_6 = "C:\WINDOWS\system32\rundll32.exe" "C:\WINDOWS\system32\fa217b17-bd53-4445-bc32-3de578a2826a_6.avi", start minimized

HKCU\..\Run, fa217b17-bd53-4445-bc32-3de578a2826a_6 = "C:\WINDOWS\system32\rundll32.exe" "C:\Documents and Settings\roger\Application Data\fa217b17-bd53-4445-bc32-3de578a2826a_6.avi", start minimized

Processes (23 whitelisted)

C:\Program Files\FreeFixer\freefixer.exe

Explorer.exe Modules (109 whitelisted)

C:\WINDOWS\system32\MSVCR71.dll

Rundll Modules (71 whitelisted)

C:\DOCUME~1\roger\LOCALS~1\Temp\wrk90.tmp

Recently created/modified files

2 minutes, c:\Documents and Settings\roger\Local Settings\Temp\wrk90.tmp

2 minutes, c:\Program Files\Antimalware Defender\Antimalware Defender.dll

2 minutes, c:\Documents and Settings\roger\Local Settings\Application Data\fa217b17-bd53-4445-bc32-3de578a2826a_6.avi

2 minutes, c:\Documents and Settings\roger\Application Data\fa217b17-bd53-4445-bc32-3de578a2826a_6.avi

2 minutes, c:\Documents and Settings\All Users\Application Data\fa217b17-bd53-4445-bc32-3de578a2826a_6.avi

2 minutes, c:\WINDOWS\system32\fa217b17-bd53-4445-bc32-3de578a2826a_6.avi

2 minutes, c:\Documents and Settings\roger\Local Settings\Temporary Internet Files\Content.IE5\6CSRVCZ7\s[2].bin


Did this help you remove AntiMalware Defender?

Saturday, 30 January 2010

MyPcSecure Scareware

MyPcSecure claims to detect malware on a clean system:


It's located in C:\Program Files\MyPcSecure Software\MyPcSecure\MyPcSecure.exe